
Your client passwords are being traded long before anyone on your team sees an alert. An infostealer infects a laptop on Monday, the logs hit a marketplace or a Telegram channel by Tuesday and a credential stuffing run starts by Wednesday. The first sign of trouble is often a login that looks perfectly normal.MSSP dark web software exists to shorten that gap. It watches criminal marketplaces, breach forums, paste sites and stealer log channels for client data, then turns what it finds into alerts your analysts can act on.
For a provider running dozens or hundreds of accounts, the right MSSP dark web software is the difference between a service you can scale and a manual research task that eats analyst hours.This guide is written as a buyer's guide rather than a how-it-works explainer. It covers what the software is, the main types on the market, the features that matter once you run more than a handful of clients, how to compare your options and the mistakes that cause providers to regret a purchase six months later.
What Is MSSP Dark Web Software?
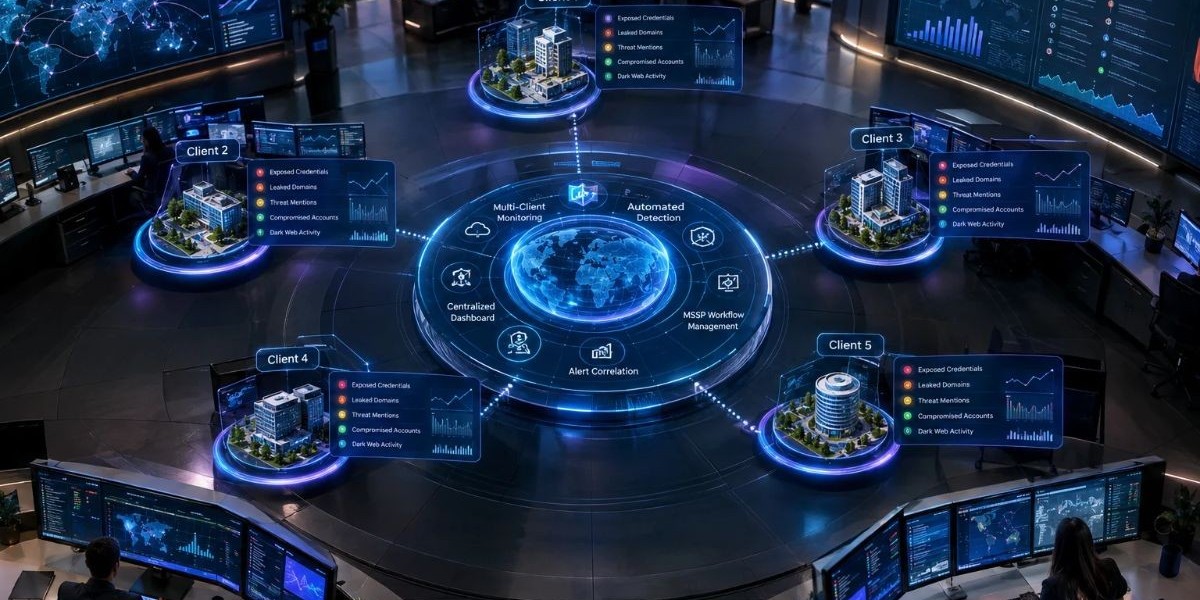
MSSP dark web software is a platform that monitors the dark web, deep web and criminal channels for exposed data tied to a provider's clients and manages that monitoring across many client organizations from one place. In practice, it combines data collection, matching, alerting and client reporting in a multi-tenant system built for service providers.
A few terms are worth separating, because vendors use them loosely:
Dark web monitoring is the act of searching hidden and semi-hidden criminal sources for your organization's data, such as leaked credentials, internal documents, or customer records.
Dark web scanning usually means a point-in-time lookup, such as checking a domain against known breach data. It tells you what is exposed today, not what appears tomorrow.
Dark web threat intelligence is broader. It covers actor activity, malware trends and attack planning, not just whether your data leaked.
MSSP dark web software wraps these capabilities in a delivery model. It adds client separation, role-based access control (RBAC), white-label reporting and workflows that fit a service provider's operations.
That last point is what separates provider-grade tools from products built for a single company's security team. A single-enterprise tool answers one question: are we exposed? A provider tool must answer that question for every client, keep their data apart and present results under your brand.
How MSSP Dark Web Software Works
The software follows a repeatable pipeline. It collects data from criminal sources, normalizes it, matches it against client assets, scores the findings and delivers alerts. Each stage affects how useful the final alert is, so it helps to know what happens at each one.
Data collection
Collection is the foundation. Platforms gather data from several kinds of sources:
Dark web marketplaces where stolen accounts and access are sold
Breach forums where leaked databases are posted or traded
Stealer log channels, often on messaging apps, where infostealer output is shared or sold
Paste sites where credentials and internal data are dumped
Ransomware leak sites where stolen files are published after an extortion attempt
No tool sees everything. Many criminal communities are invite-only and sources appear and vanish quickly. Be wary of any vendor that claims total coverage. A better question to ask is which source types they cover and how they handle sources going offline.
Normalization and enrichment
Raw data is messy. A stealer log might contain thousands of lines of browser data, saved passwords, cookies and system details in inconsistent formats. The software parses these files, extracts the useful fields and attaches context such as the source, the date it was first seen and whether the data looks new or recycled from an older breach.
Without this step, analysts end up reading raw dumps. With it, they see a clean record: this email, this service, this type of exposure, first seen on this date.
Asset matching
Next, the platform matches collected data against what each client has told it to watch. The usual watch items are:
Email domains
Executive and VIP names or email addresses
Brand names and product names
IP ranges and hostnames
Specific high-value accounts
Domain-level matching is the workhorse for credential exposure. If a client owns example-client.com, any leaked record with an address on that domain becomes a candidate alert. Better platforms also check whether the credentials are plaintext, hashed, or paired with session cookies, since each carries a different level of risk.
Scoring and alert delivery
Once a match is confirmed, the platform scores it. Good scoring considers freshness, data type, whether a password is exposed in cleartext and whether the record appears tied to an active infection. It then routes the alert to the right place: a dashboard, an email digest, a ticketing system, or a SIEM or SOAR connection.
For an MSSP, routing matters as much as detection. An alert that lands in the wrong client's queue, or a shared inbox nobody owns, is a failure even if the detection was perfect.
Why MSSPs Need Dark Web Monitoring Software
Providers need dark web software because credential theft is one of the most reliable ways attackers get in and clients expect their provider to catch it. Manual searching does not scale and a missed exposure turns into an incident that lands on your desk.
Here is how the pressure shows up in day-to-day service delivery.
Credential theft is a primary entry route
Industry breach reports, including the annual Verizon Data Breach Investigations Report, have repeatedly listed stolen credentials among the most common ways attackers gain initial access. Attackers like valid logins because they blend in. MITRE ATT&CK tracks this behavior under the Valid Accounts technique, which highlights how often adversaries use real accounts rather than noisy exploits.
Infostealers feed the market
Infostealer malware harvests saved passwords, browser cookies and session tokens from infected devices. Those logs are packaged and sold or shared in bulk. For a provider, this changes the picture: a client does not need to be breached themselves for their credentials to appear. An employee's personal laptop, infected while the employee used a work login, can be enough.
Clients want proof, not promises
Security buyers increasingly ask providers to show visible, ongoing coverage. A dark web monitoring service gives you something concrete to show: a report listing exposures found, actions taken and risk reduced. That is easier to defend in a renewal meeting than a general claim about vigilance.
It opens a new revenue line
Dark web monitoring slots neatly into existing packages. Providers can bundle it with managed detection and response, offer it as an add-on, or use it to open conversations with prospects. Because the software can be white-labeled, the service appears as part of your own portfolio.
Manual research does not scale
An analyst can check a few domains by hand. Nobody can do that weekly for eighty clients across forums and stealer channels. Software turns a research chore into a background process, so your people spend time on response instead of searching.
Types of MSSP Dark Web Software
Providers usually choose among four approaches. Each has a real use, but they differ sharply in how well they handle many clients at once. Understanding the categories helps you avoid buying a product that was never designed for your model.
Free and consumer-style breach checkers
These tools let you enter an email or domain and see whether it appears in known breaches. Services such as Have I Been Pwned, created by security researcher Troy Hunt, are valuable for awareness and quick checks. They are not built for service delivery. They typically lack client separation, continuous alerting at scale, branded reporting and the audit trail a paid service needs.
Enterprise threat intelligence platforms
Large threat intelligence products offer deep coverage and rich analyst tooling. They suit organizations with in-house threat intel teams who will read the reports and run investigations. For many MSSPs, they bring more than the service needs, along with the cost and training that come with that depth. They may also lack the white-label and per-client controls that a provider requires.
Purpose-built, multi-tenant MSSP platforms
These are built for the provider model from the start. They offer separate client workspaces, RBAC, branded reports and a way to onboard a new client quickly. This category is where the term white-label dark web monitoring software applies most directly. If you plan to sell dark web monitoring as part of your own offering, this is usually the closest fit.
Build-it-yourself with open data and scripts
Some technically strong teams assemble their own tooling from public breach data, scraper and custom matching scripts. It can work for a narrow need. The hidden costs are source access, legal and safety questions around collecting criminal data, constant maintenance as sources change and the lack of a polished client-facing layer. Most providers find the time is better spent on delivery.
Key Features to Look For in MSSP Dark Web Software
The most important features are the ones that make multi-client operation practical: multi-tenancy, RBAC, white-label reporting, low-noise alerting and integrations. Detection quality is expected. Operational fit is what separates a good purchase from a frustrating one.
Multi-tenant architecture
Each client should live in a separate workspace with its own assets, alerts and users. Data from one client must never appear in another's view. Ask how tenant separation is enforced and whether you can manage all tenants from one provider-level console. Good MSSP dark web software should let you onboard a new client quickly instead of spending days on manual setup.
Role-based access control
Your analysts, account managers and client contacts need different views. RBAC lets you give an analyst access to many clients, a client contact access to only their own data and a read-only role to auditors or executives. Without it, you will end up sharing logins, which is a risk in itself.
White-label branding
If the service goes out under your name, the dashboards and reports should too. Check whether you can add your logo, colors and custom domain and whether exported reports carry your branding without vendor marks.
Credential and exposure coverage
Look for coverage across the exposure types that matter most: leaked credentials, stealer log data, mentions of executives, domain or brand impersonation signals and leaked documents. Ask whether the platform distinguishes plaintext from hashed passwords and whether it flags exposures tied to recent infections.
Alert quality and noise control
Too many alerts and your analysts stop reading them. Look for deduplication, severity scoring, freshness indicators and the ability to mark an alert as resolved or false positive so it does not return. A short, trustworthy alert queue is worth more than a long one.
Integrations and automation
Alerts should flow into the tools your team already uses. Common needs include ticketing systems, SIEM and SOAR platforms, chat notifications and an API for custom workflows. An API also lets you pull data into your own client portal or reports.
Reporting for clients
Clients rarely log into a security dashboard. They read reports. Look for scheduled, branded summaries that explain what was found, how serious it is and what was done. Reports that translate technical findings into plain business language save your account managers hours.
Onboarding and scalability
Ask how long it takes to add a client, whether bulk onboarding is available and how pricing scales with the client count. Ask for a pricing structure in writing rather than assuming one, since models vary between vendors and can change as you grow.
Transparency about sources
A trustworthy vendor can explain, at least in general terms, what kinds of sources they monitor and how often. They should also be honest about limits. Claims of seeing the entire dark web are a warning sign.
Comparison of MSSP Dark Web Software Approaches
The table below compares the four common approaches across the factors that matter most to a provider. Use it as a starting point for your own scoring and adjust the weighting to match your client base and team skills.
Factor | Free breach checkers | Enterprise threat intel platforms | Purpose-built MSSP platforms | In-house build |
Designed for multiple clients | No | Sometimes, depending on the product | Yes | Only if you build it |
White-label reporting | No | Limited or varies by vendor | Typically included | Custom work required |
Continuous monitoring and alerts | Limited or manual | Yes | Yes | Depends on your tooling |
RBAC and client workspaces | No | Varies | Yes | Custom work required |
Analyst effort to run | High, mostly manual | High, needs threat intel skills | Low to moderate | High, ongoing maintenance |
Best suited for | Quick awareness checks | Teams with dedicated intel analysts | Providers selling a monitoring service | Teams with unusual or narrow needs |
Main limitation | No service delivery layer | Depth may exceed what the service needs | Coverage varies by vendor, so verify it | Source access, safety and upkeep burden |
Deployment and Packaging Models
Once you pick a platform, you still decide how to sell it. The same software can support several packaging models and the right one depends on your client mix.
Bundled into a managed service. The monitoring is included inside a larger package, such as MDR. It raises the value of the package and reduces churn, but you absorb the cost.
Sold as an add-on. Clients opt in for an extra fee. This keeps the base package clean and makes the revenue easy to track.
Used as a prospecting tool. Many providers run a limited exposure check for a prospect and use the findings to open a conversation. Make sure the results are accurate and that you have permission to assess the domain before sharing anything.
Offered as a one-time assessment. Useful for clients who are not ready for a subscription. It also works as a first step toward ongoing monitoring.
Whichever model you pick, decide up front who owns the alert response. Will your analysts handle it, or will you hand the client a recommendation and let them act? Clear ownership prevents the awkward situation where an exposure sits in a dashboard because everyone assumed someone else would act.
An Evaluation Checklist for Choosing MSSP Dark Web Software
Use this checklist during demos and trials. A vendor who answers these clearly is usually a vendor who understands providers.
Can I manage every client from a single provider console, with strict data separation between tenants?
Does the platform support RBAC for analysts, client contacts and read-only users?
Can I white-label dashboards, alerts and reports, including a custom domain?
Which source types does the platform cover and how does it handle sources that disappear?
Does it separate plaintext credentials from hashed ones and flag exposures linked to infostealer activity?
How are alerts scored, deduplicated and marked as resolved?
What integrations and API options are available for ticketing, SIEM and SOAR?
How long does it take to onboard a new client and is bulk onboarding supported?
How is pricing structured and how does it change as my client count grows?
What does the vendor offer for support, training and sales enablement?
Can I run a trial using real client domains, with permission, before I commit?
What happens to my data and my clients' data if I leave the platform?
Score each answer, weigh the items that matter most to your business and compare vendors on the same sheet. A written scorecard also helps when you explain the decision to a partner or manager.
Common Mistakes When Buying MSSP Dark Web Software
Most poor purchases share a few causes. Watching for them will save you time and money.
Choosing on coverage claims alone. A vendor that promises to see everything cannot prove it. Judge them on how clearly they describe their sources and limits, then test with a pilot.
Ignoring the client-facing layer. Detection is only half the product. If reports are hard to read or cannot carry your branding, your account managers will build their own and that cost adds up fast.
Buying a single-enterprise tool for a multi-client job. These tools often lack tenant separation, which creates both an operational problem and a privacy risk.
Skipping the alert workflow. A platform that sends alerts to an email nobody owns is not a service. Define who triages, who contacts the client and how fast.
Not testing alert noise. Run the trial long enough to see how many alerts are duplicates or recycled breach data. High noise erodes analyst trust.
Forgetting consent and scope. Only monitor domains and assets that a client has authorized you to watch. Put the scope in the contract.
Overpromising to clients. Dark web monitoring reduces risk, but it does not prevent breaches by itself. Position it as an early warning layer that works alongside MFA, endpoint protection and password hygiene.
Interesting Facts and Key Stats
These points come from widely cited public sources. Exact figures change with each annual edition, so check the latest report before quoting a number to a client.
According to the Verizon Data Breach Investigations Report, stolen credentials have repeatedly ranked among the leading ways attackers gain initial access to networks.
IBM's annual Cost of a Data Breach research has repeatedly found that breaches starting with stolen or compromised credentials are among the harder ones to detect and contain. IBM publishes updated figures every year.
MITRE ATT&CK catalogs the use of valid accounts as a standard attacker technique, which reflects how often real logins are used instead of exploits.
NIST Special Publication 800-63B recommends that systems check chosen passwords against lists of known compromised passwords, which shows how mainstream the idea of using breach data for defense has become.
Have I Been Pwned, run by security researcher Troy Hunt, has long served as a public index of breached accounts, showing how widespread credential exposure is.
The dark web is reached through special software such as Tor and makes up a small portion of the overall internet, yet it hosts a meaningful share of the marketplaces and forums where stolen data is traded.
Conclusion
MSSP dark web software gives providers a repeatable way to find exposed credentials and sensitive data before attackers use them and to prove that work to clients. The strongest platforms are the ones built for service delivery: multi-tenant, RBAC-based, white-label and quiet enough that analysts trust the alerts they see.If you are ready to compare platforms built around this provider model, take a look at what Mispar offers for MSSPs and see whether it fits the way your team delivers service.
Frequently Asked Questions (FAQs)
What is MSSP dark web software?
MSSP dark web software is a multi-tenant platform that monitors the dark web and other criminal sources for client data, such as leaked credentials and delivers alerts and reports across many client organizations from one console. It adds features providers need, including RBAC and white-label reporting.
How is MSSP dark web software different from a regular dark web monitoring tool?
A regular tool is built for one organization's security team. MSSP dark web software is built to manage many clients at once, with separate workspaces, role-based access, branded reports and client onboarding workflows that suit a service provider.
What data does dark web monitoring software look for?
It typically looks for leaked credentials, infostealer logs, exposed documents, mentions of executives or brands and data from breach forums, marketplaces, paste sites and ransomware leak sites. Coverage varies by vendor, so ask which source types are included.
Can MSSPs white-label dark web monitoring?
Yes, many purpose-built platforms support white-labeling, including custom logos, colors and branded reports. Confirm the details with each vendor, since the depth of white-label options, such as custom domains, differs between products.
How do I choose the best dark web monitoring software for my MSSP?
Start with multi-tenancy, RBAC, white-label reporting, alert quality and integrations. Use a written checklist, test with real client domains under authorization and compare how clearly each vendor explains its sources and limits.
Does dark web monitoring prevent data breaches?
No. It acts as an early warning layer that helps you find exposed credentials and data sooner so you can reset passwords, revoke sessions and warn the client. It works best alongside MFA, endpoint protection and strong password practices.